See the incident.
Not the alert queue.
LuceraAI investigates every alert across your security stack with a council of specialist AI agents. Its deep, unique knowledge of your organisation's habits shapes every verdict. It explains its reasoning and responds within the limits you set.
Too many alerts. Not enough hours.
Always on.
2am alerts don’t wait for office hours, and covering nights and weekends costs time, sleep or another provider.
Too much noise.
False positives eat the time meant for real threats, and dispersed tooling means hopping between consoles to piece each one together.
New threats, fast.
Attacks move quickly, and analysts often learn each new technique on the job, which slows response.
Untapped tools.
You’ve invested in EDR, identity and email security, but investigating what they raise is still manual.
Your unique context behind every verdict.
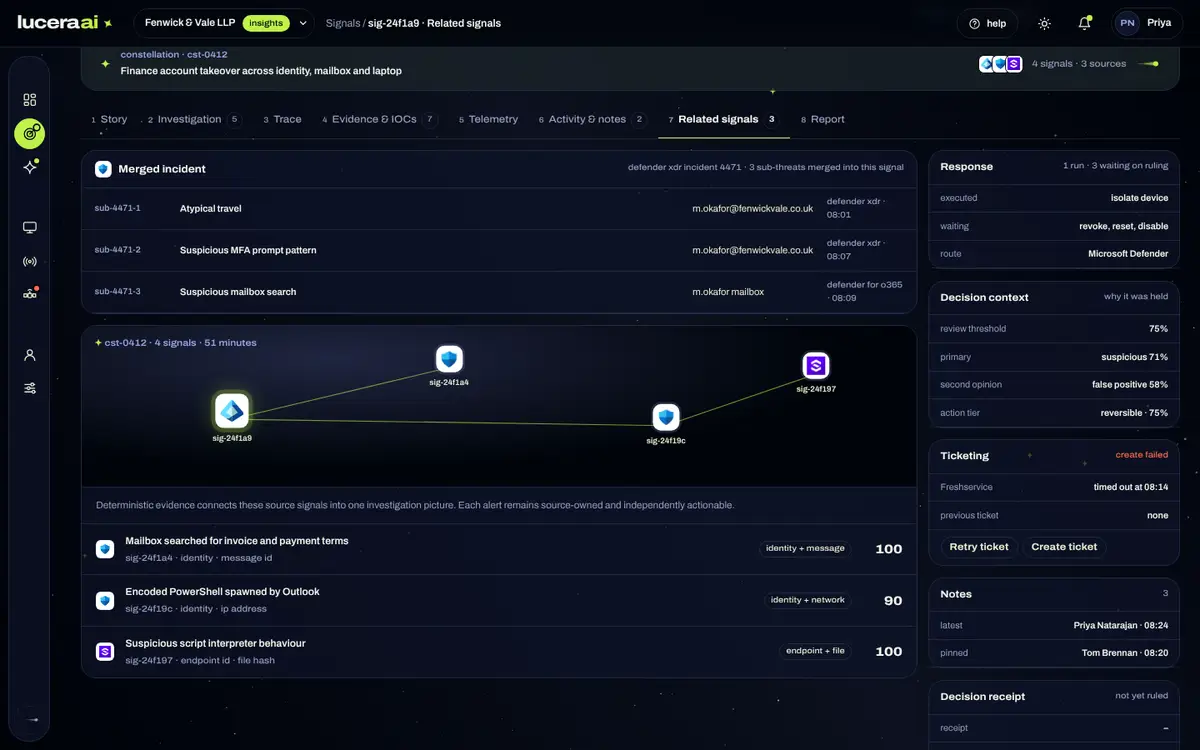
An alert on its own says very little. Is that tool routine for your finance team? Has that device behaved like this before? Did your analysts rule on something similar last month? Star Chart, LuceraAI’s living map of your organisation, answers those questions before a verdict is made.
LuceraAI learns your environment from every signal it investigates: your software, your people, your devices and how they relate. Then it brings that context to every decision.
- What's normal for you. Your industry, your size and the software that's routine for an organisation like yours, so a tool your team runs every day isn't treated as a stranger.
- How everything connects. Identities, devices, IP addresses, domains, files and processes, how often each has been seen, and which verdicts they were part of.
- How your team decides. Every analyst ruling is remembered. An overturned pattern pauses automatically, so LuceraAI learns from your judgement rather than replacing it.
- Context you can check. Every fact shows where it came from: your tools, your analysts, or what LuceraAI learned.
The longer it runs, the better it knows you, and the sharper every verdict gets.
Every signal investigated, every decision explained.
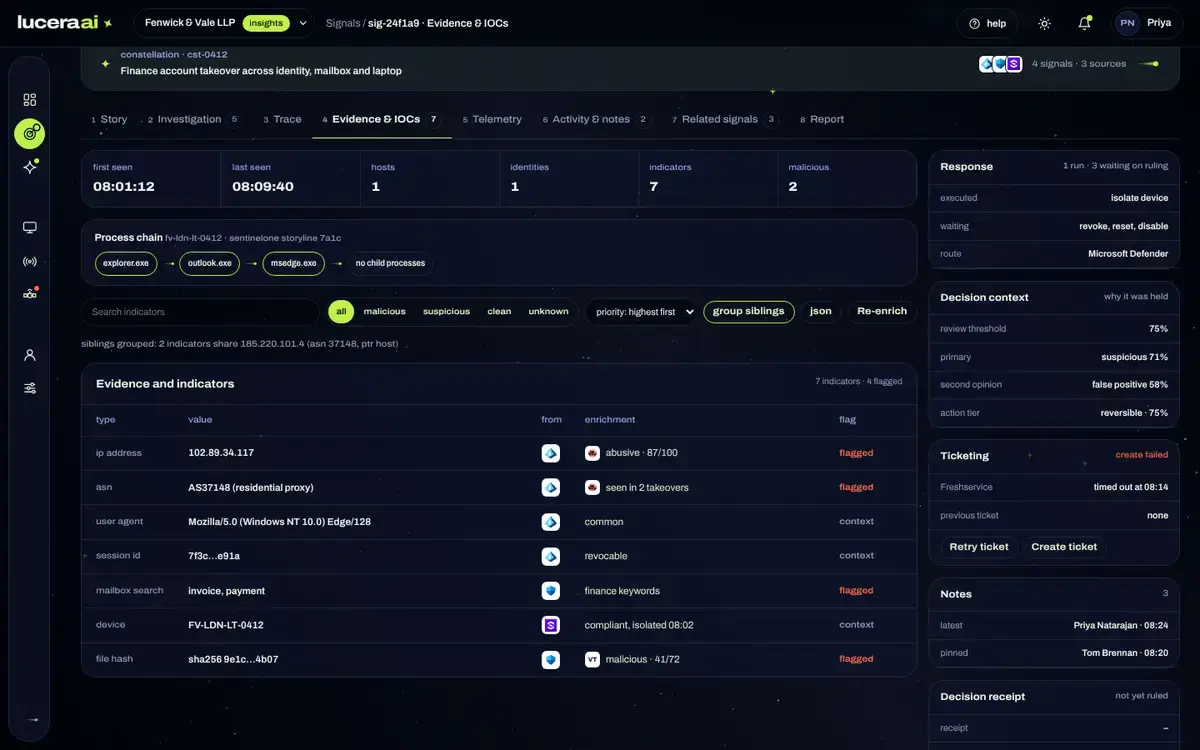
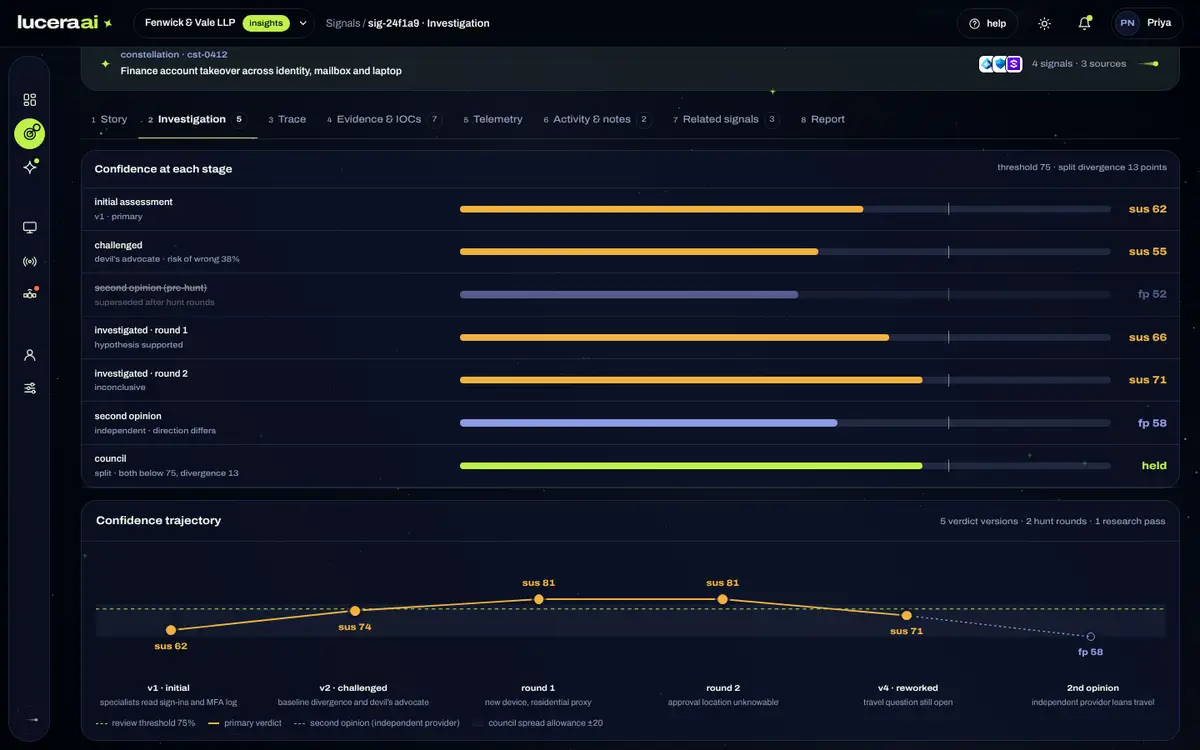
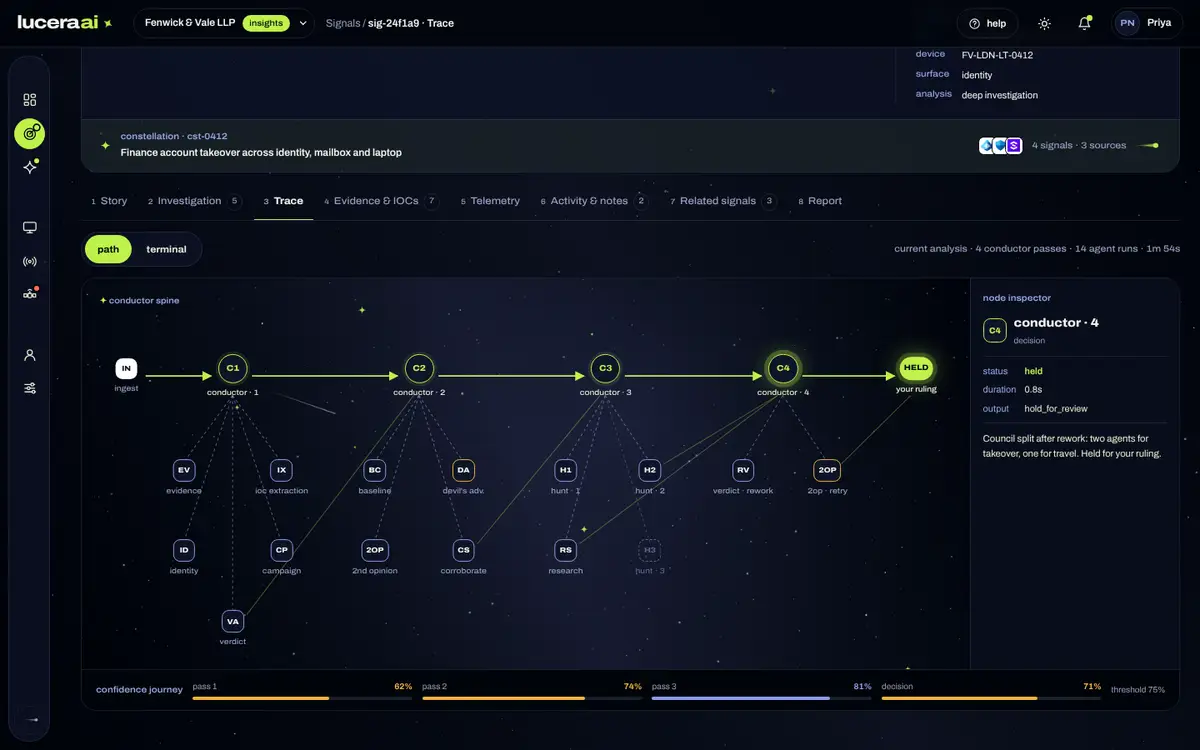
LuceraAI sits on top of the security tools you already own and investigates every signal they raise, the moment it arrives. A council of specialist AI agents gathers the evidence, hunts for more, challenges its own verdict and gets a second opinion from an independent model. Along the way it builds a deep understanding of your organisation: the software that's routine for you, how your people, devices and accounts normally behave, and how your team has ruled before. Every new signal is weighed against that, so its verdicts sharpen over time. Then it acts within the limits you set, or hands a person the full case.
Not a SIEM, and not a replacement for your EDR. A force multiplier for the team you have.
From signal to decision in five steps.
- 1
Gather the evidence.
Specialist agents collect the evidence, a baseline of what’s normal and the indicators of compromise.
- 2
Corroborate the verdict.
A devil’s advocate challenges it, and an independent model gives a second opinion.
- 3
Test it with a hunt.
LuceraAI searches for the evidence that would prove or disprove it.
- 4
Recheck.
The verdict is reworked against everything the hunt found.
- 5
Decide and act.
Within your rules, or escalated to a person.
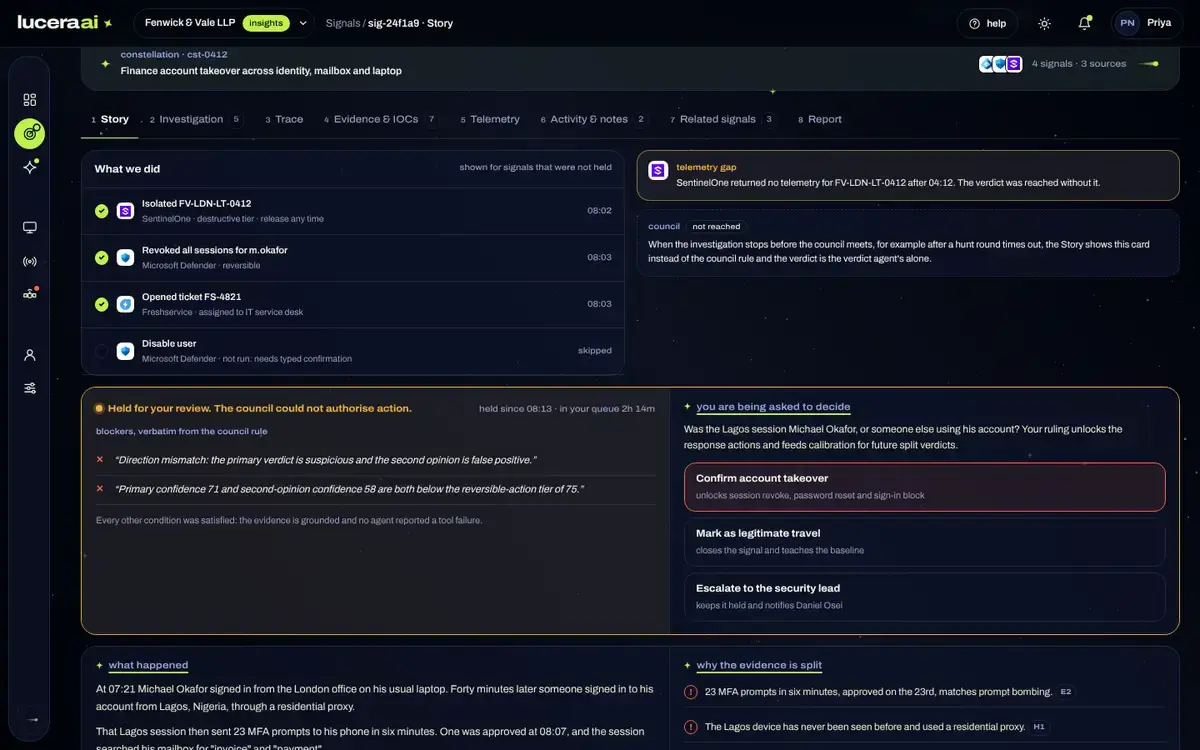
Context-aware decisions start with knowing every device.
- Records from tools like SentinelOne, Microsoft Defender, Intune, CrowdStrike Falcon and Cloudflare WARP are matched into a single device.
- Compare any two sources to see which devices one tool has missed, such as laptops with no EDR agent.
- A signal is raised when a device falls outside the coverage policy you set.
- Device context feeds every verdict: knowing what a device is helps the council judge what it sees.
Works with the tools you already own.
 alerts and response
 alerts and response
 enrichment
 tickets
 tickets
 notifications
 asset source
 asset source
 asset source
 alerts and responsealerts and responseenrichmentticketsticketsnotificationsasset sourceasset sourceasset source
Wherever you are with AI, there is a sensible place to start.
I'm ready to put AI to work.
Start in Insights, watch the investigations land, and move sites to Orchestrate as your confidence grows.
Get started →
I'd like to see it prove itself first.
Start in Observe on your own alerts. Nothing acts on your estate, and you get the evidence and our method notes to judge it.
Show me →Adopt AI at your own pace, with a record you can defend to the board.
Every alert investigated, so your analysts work the cases that need judgement.
The evidence is gathered for you, and you can see exactly why each verdict was reached.
Every alert looked at, even at 2am, with a plain-English answer.